Is executed by Wolfcore, not an automated marketing platform
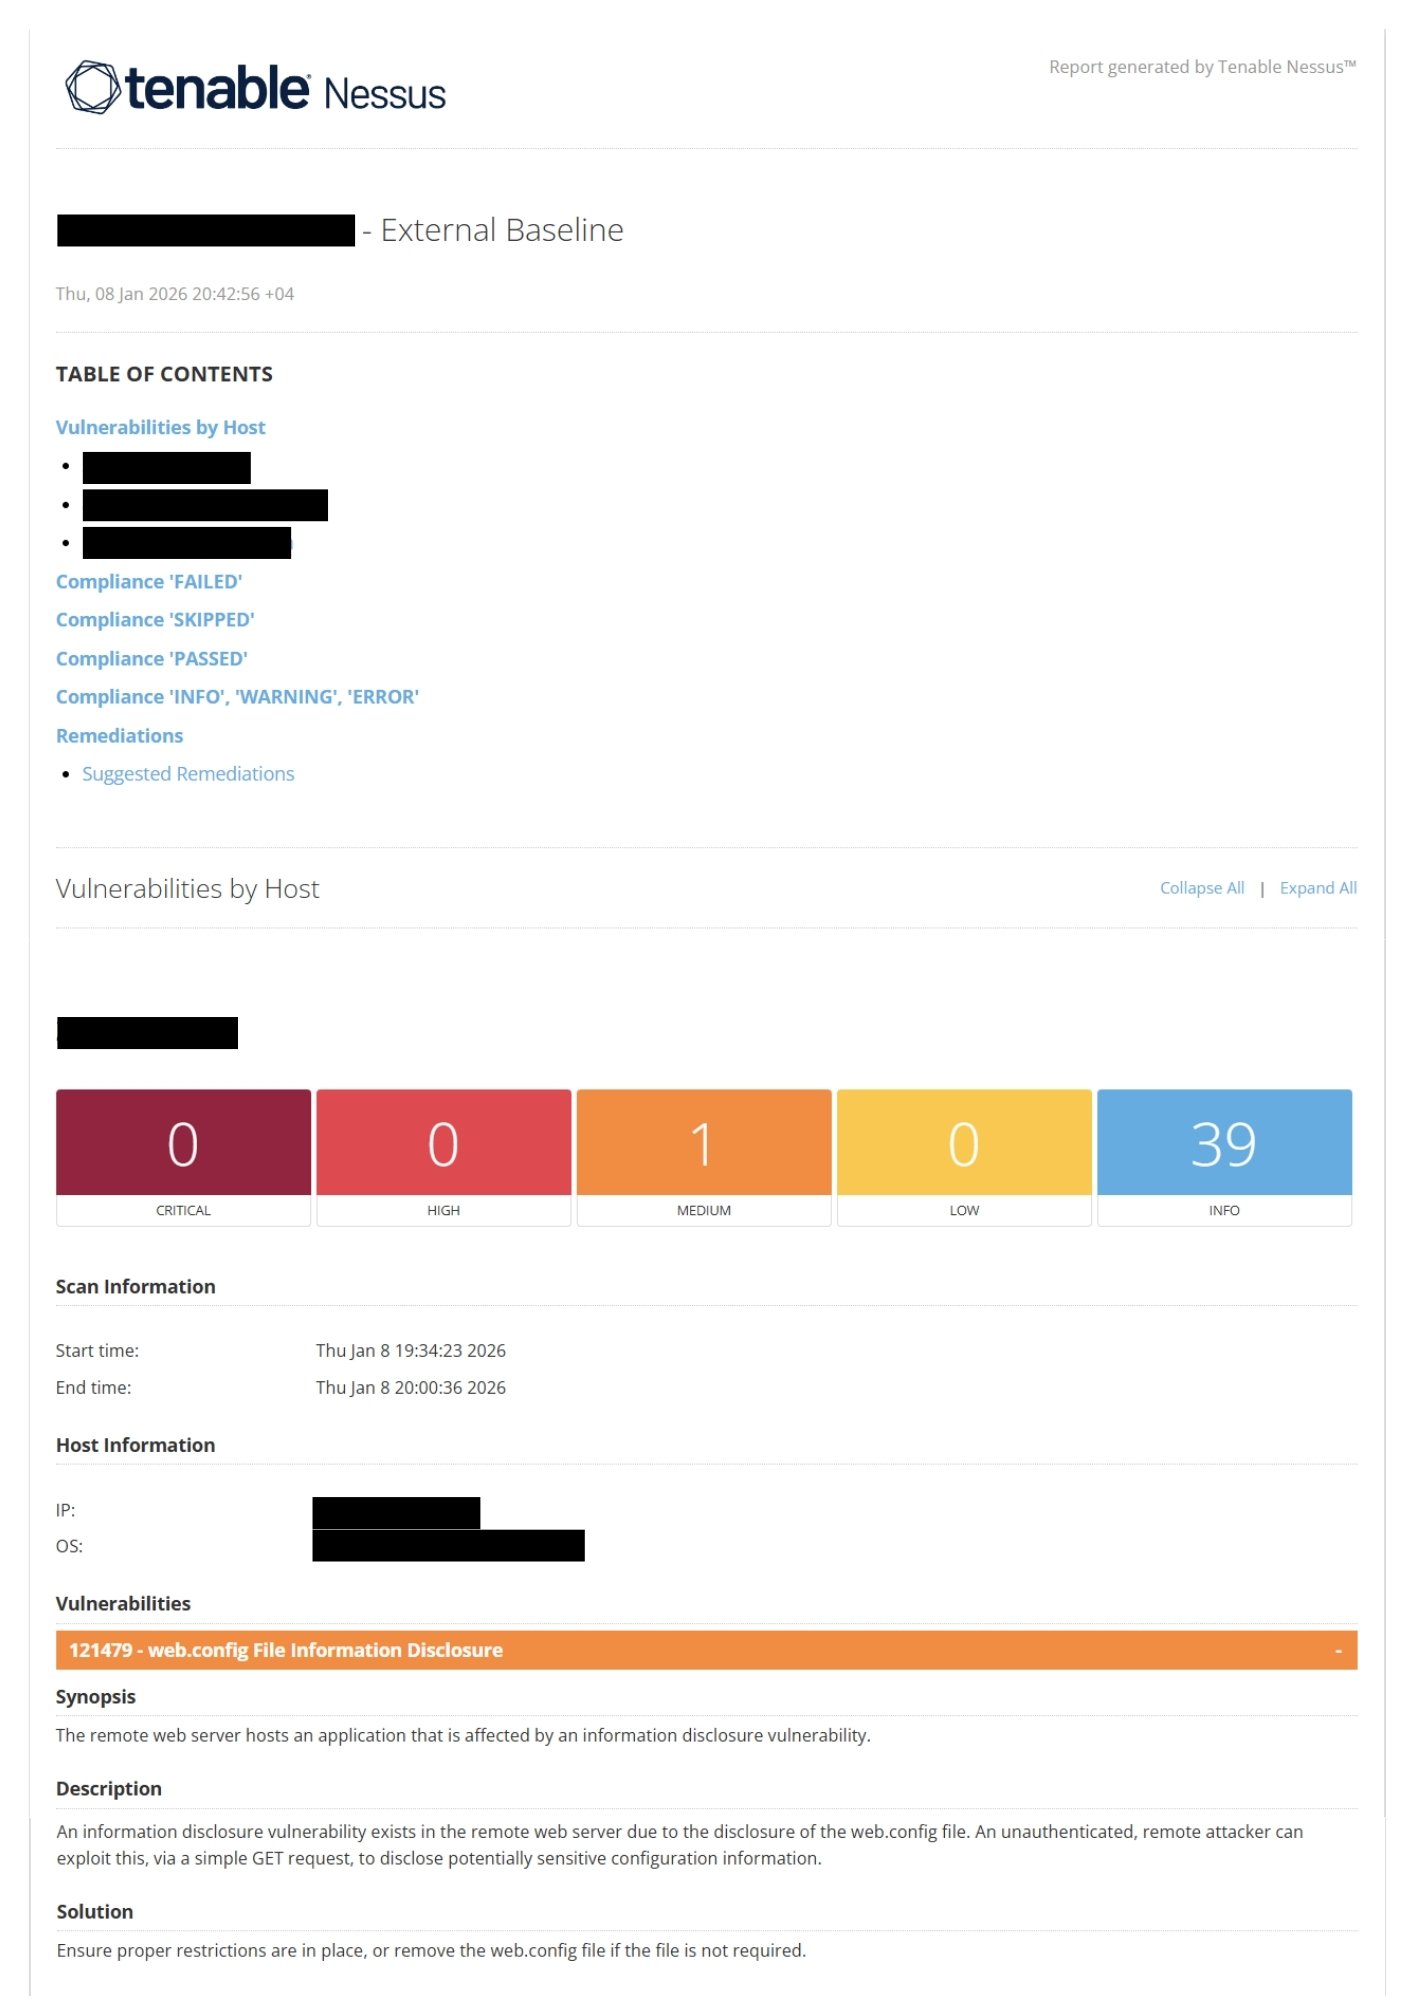
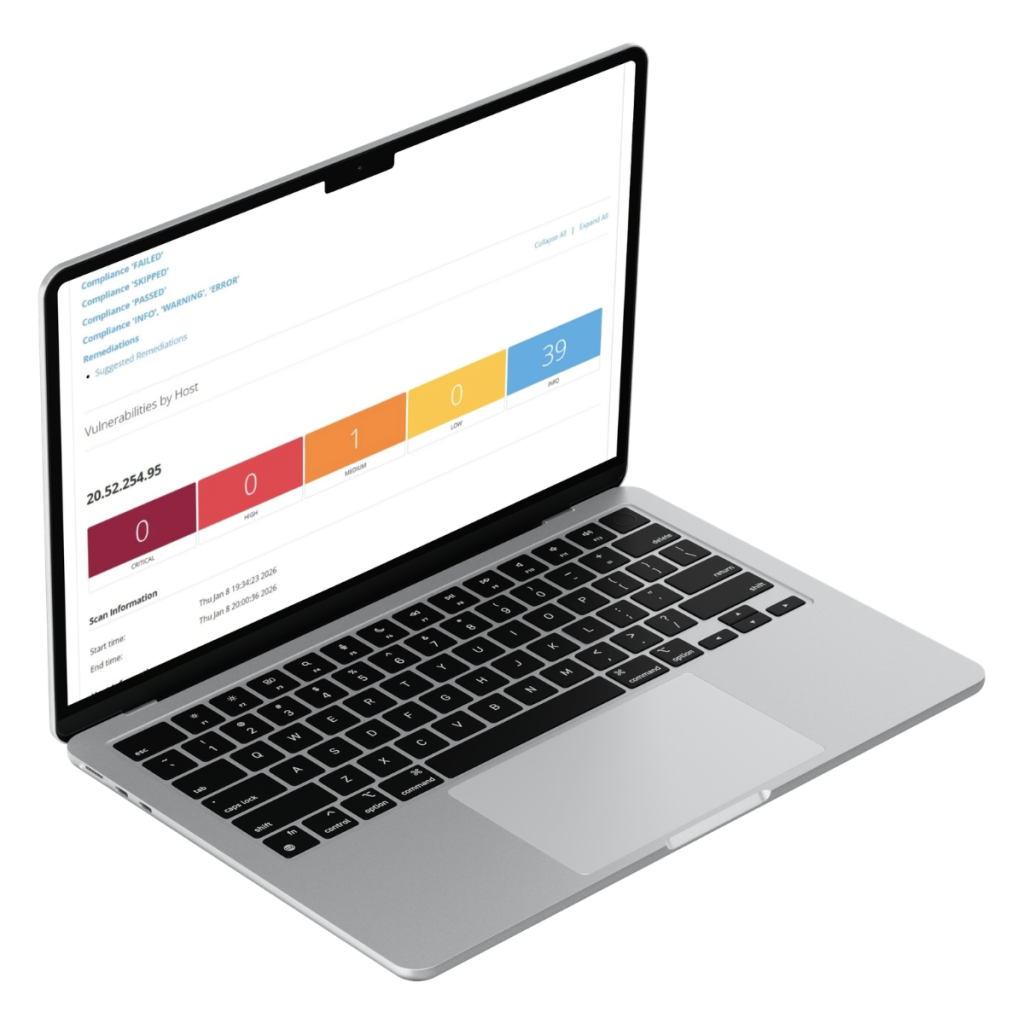
Provides the full technical report
Reflects professional tooling used in commercial engagements
Request your free external vulnerability scan.
By requesting a free scan, you agree to be contacted with your results and recommendations*.
What the free scan finds — and what comes next
Your free scan reveals what's externally exposed to attackers: open services, known vulnerabilities and misconfigurations on your internet-facing systems. It's the perfect first step. When you need deeper assurance — authenticated testing, business-logic flaws and proven exploitation — a full penetration test is the natural next move.
An external scan of your internet-facing systems for known vulnerabilities, exposed services and common misconfigurations, delivered as a clear summary report you can act on.
Is the free scan really free?
Yes — completely free and with no obligation. It's a fast, low-friction way to see what attackers can see from the outside.
How is the free scan different from a penetration test?
The free scan is automated and external-only. A full penetration test adds manual exploitation, authenticated testing and business-logic checks to prove which issues are genuinely exploitable.
How do I get my results?
Once you request the scan, we run it against your external systems and send you a clear report, usually within a few business days.
What should I do after the scan?
Fix the quick wins it surfaces, and for anything serious or business-critical, book a full penetration test or talk to our team.
Scope clarification
This scan is:
External only
Automated vulnerability scanning
Focused on publicly accessible systems
Designed to provide a technical baseline
This scan is not:
A full penetration test
Manual exploitation
Authenticated testing
Business logic testing
Internal network assessment
A prioritised remediation plan
If you require deeper security testing or contextual analysis, Wolfcore can discuss structured penetration testing separately.